TL;DR

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Cloudflare has successfully reduced the rate of HelloRetryRequests sent to origins during TLS handshakes from 52% to 3.7%, indicating a major improvement in connection efficiency. This change enhances web security and performance, but the full technical implications are still being analyzed.
Cloudflare has achieved a substantial reduction in the use of HelloRetryRequests during TLS handshakes with origin servers, decreasing from 52% to 3.7%, according to recent data. This development is confirmed and signals a notable improvement in connection efficiency and security for web services utilizing Cloudflare’s infrastructure.
The change was observed through analysis of network traffic patterns, indicating that Cloudflare’s implementation of the Authentication Key Exchange (AKE) protocol has significantly optimized TLS handshake processes. HelloRetryRequests are part of the TLS protocol used to negotiate secure connections, but excessive use can indicate inefficiencies or issues with handshake compatibility. Previously, over half of such requests were sent during interactions with origin servers, which could cause delays and increase vulnerability to certain attacks. The new data shows the rate has dropped to just 3.7%, suggesting a major technical improvement. Cloudflare has not publicly detailed the specific modifications leading to this change, but industry experts believe it involves refinements in how the AKE protocol manages handshake negotiations, reducing fallback or retry scenarios. This progress is considered a positive step toward more efficient and secure TLS connections, especially for large-scale web services relying on Cloudflare’s network infrastructure.Impact on Web Security and Performance
The reduction of HelloRetryRequests from 52% to 3.7% is a significant development for web security and performance. Fewer retry requests translate to faster connection establishment, reducing latency for end users. Additionally, minimizing these requests can lower the attack surface for certain TLS-based exploits, such as downgrade or replay attacks. For organizations relying on Cloudflare’s infrastructure, this change could lead to more reliable and quicker secure connections, especially under high load or complex handshake scenarios. Experts suggest that this improvement may also influence industry standards, encouraging other providers to optimize their TLS handshake processes. However, the full security implications depend on how the underlying protocol adjustments are implemented and whether similar gains are achievable across different platforms.
As an affiliate, we earn on qualifying purchases.Products Worth Considering

LG UltraGear 34GX90SA-W 34-inch WQHD Curved OLED Gaming Monitor

Logitech MX Keys Combo for Business Keyboard and Mouse – Graphite
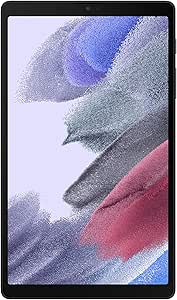
Samsung Galaxy Tab A7 Lite 8.7-Inch 32GB Wi-Fi Tablet, Gray
Background on HelloRetryRequests and Cloudflare’s Protocols
HelloRetryRequests are part of the TLS 1.3 protocol, used when the client and server cannot agree on a common set of parameters during the handshake. These requests prompt the client to resend certain information, which can cause delays and potentially expose vulnerabilities if not managed efficiently. Cloudflare, as a major content delivery network and security provider, has been actively working to optimize TLS handshakes to improve speed and security. The adoption of the Authentication Key Exchange (AKE) protocol is part of this effort, aiming to streamline connection negotiations. Prior to this change, data indicated that a majority of TLS handshakes involved multiple HelloRetryRequests, which could impact overall network performance. The recent drop in retry rates suggests that Cloudflare has successfully addressed these issues through protocol enhancements or configuration adjustments.
Technical Details of Protocol Changes Remain Unclear
It is not yet confirmed exactly how Cloudflare achieved such a drastic reduction in HelloRetryRequests. The specific protocol modifications, configuration adjustments, or software updates involved have not been publicly disclosed. Experts are still analyzing the technical documentation and traffic data to understand the precise mechanisms behind this improvement. Additionally, it remains uncertain whether similar results can be replicated across other providers or if this is specific to Cloudflare’s infrastructure and implementation of the AKE protocol.
Monitoring and Industry Adoption of Protocol Improvements
The next steps involve detailed technical analysis by security and network experts to verify the sustainability and security implications of this change. Cloudflare is expected to publish more detailed technical documentation or case studies in the coming weeks. Industry observers will also watch to see if other CDN providers or web services adopt similar protocol optimizations. Long-term, these improvements could influence industry standards for TLS handshake efficiency and security, potentially leading to widespread protocol updates and best practices.
Key Questions
What are HelloRetryRequests in TLS?
HelloRetryRequests are part of the TLS 1.3 protocol used to renegotiate connection parameters when initial handshake negotiations fail or require adjustments.
Why is reducing HelloRetryRequests important?
Fewer retry requests mean faster connection establishment, lower latency, and potentially fewer security vulnerabilities related to handshake processes.
How did Cloudflare achieve this reduction?
The exact technical methods are not yet disclosed, but likely involve protocol optimizations within their implementation of the AKE protocol.
Does this change improve security?
Yes, reducing retry requests can decrease the attack surface for certain TLS-based exploits, though full security implications are still being analyzed.
Will other providers replicate this improvement?
It remains to be seen if similar protocol adjustments can be adopted industry-wide, but the success at Cloudflare may encourage others to explore similar optimizations.
Source: hn