🔍 Read the full analysis: AI Chat Privacy In Focus After Notion’s Fireworks Breach Report on ThorstenMeyerAI.com

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
TL;DR
Notion says attackers accessed a Fireworks AI dataset containing stored Notion AI chat transcripts associated with its Insights feature. The company says fewer than 1% of workspaces are affected and that Fireworks retained data despite a contractual zero-data-retention commitment; the system involved and retention period have not been disclosed.
Notion says a dataset accessed by attackers in the Fireworks AI breach included stored Notion AI chat transcripts used for its Insights feature, and that Fireworks retained data despite a contractual zero-data-retention commitment. Notion says fewer than 1% of workspaces are affected and reports that it revoked exposed Notion API keys found in affected user messages on November 11.
The transcripts were associated with Insights, a feature that gives workspace administrators information about how teams use AI. Notion says Fireworks provided it with a dataset on November 8 that included transcripts from the feature. It describes most affected workspace transcripts as “unattributable”, meaning they were not labeled with the author or originating workspace and did not include tool-call results. That does not mean the text was necessarily harmless: Notion defines a transcript as model input or output written to the chat, which may include sensitive information entered by a user.
Notion said the affected data should be reviewed as if it were exposed. It advises affected users and workspace owners to examine the material and rotate passwords, API keys and other credentials that may have been pasted into Notion AI during the incident. On November 11, Notion said it revoked exposed Notion API keys found in affected user messages. The company says it has not identified a workspace as affected if neither the user nor its owner has received a notice from Notion.
Notion says AI Meeting Notes were not affected unless their audio, transcripts or summaries were used as input in a Notion AI chat transcript. It also says no other Notion features were affected. These statements describe the company’s current account of the incident; the notice does not identify how many individual users are involved or detail the contents of each exposed transcript.
Notion’s Fireworks breach report puts AI chat privacy in focus
Notion says attackers accessed stored AI chat transcripts used for its Insights feature. The incident highlights the need to review vendor data practices and treat affected chat content as exposed.
What the dataset contained
Notion says the accessed dataset included stored requests and responses used for Insights.
Prompts and responses
Transcript text may include sensitive information entered by a user or generated by the model.
Mostly unattributable
Most affected transcripts lacked author and workspace labels and did not include tool-call results.
How the incident unfolded
Notion’s account traces the discovery from an initial alert to expanded customer guidance.
What customers should do
Notion advises affected users and workspace owners to review the material as if it were exposed.
Examine the relevant transcripts; missing identity labels do not mean the text is harmless.
Change passwords, API keys, and other credentials that may have been pasted into Notion AI chats.
Follow Notion’s Security incident review guidance if you or your workspace owner received a notice.
What remains unresolved
The published accounts leave important details about retention and scope open.
- Which Fireworks system retained the data
- How long the data was retained
- Exact workspace and affected-user totals
- How many transcripts contained sensitive information
- Fewer than 1% of workspaces affected
- AI Meeting Notes were not affected unless used as chat input
- No other Notion features were affected
- Critical vendors and data processors are being audited
What the Retained Chats Could Reveal
The incident puts attention on the difference between live model requests and stored product data. Notion says its zero-data-retention commitments for model vendors apply to API requests used to generate Notion AI responses, but are not intended to cover data retained to provide features such as chat history and Insights. For Insights, Notion says it sent stored requests and responses to Fireworks for analysis.
That distinction matters to organizations using AI tools for work. A user may include customer details, contract information or credentials in a prompt, and Notion says chat transcripts can contain the text entered or generated. Even where transcripts are not labeled with a person or workspace, their contents may still be sensitive or recognizable. Notion recommends examining affected data rather than assuming the lack of identifying labels makes it safe.
The disclosures also raise a vendor-governance issue: a contractual commitment is not, by itself, proof that data was not retained. Notion says it is auditing critical vendors and data processors for data-minimization practices, including zero-retention policies. The practical consequence for customers is that they need to follow the incident guidance while the companies clarify how the retention occurred.
Products Worth Considering
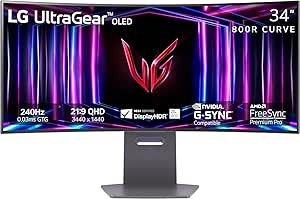
LG UltraGear 34-inch Curved OLED Gaming Monitor, WQHD 1440p, 240Hz, 0.03ms, 800R

Logitech MX Mechanical Wireless Illuminated Keyboard, Tactile Quiet, Graphite

Apple Watch Series 12 GPS 42mm
As an affiliate, we earn on qualifying purchases.
How Insights Data Reached Fireworks
Notion says it used Fireworks for two purposes: running classification jobs for Insights and providing open-weight models for inference within Notion. The dataset at issue came from the Insights side, according to Notion. The company says Fireworks sent it the dataset on November 8 and that it contained stored Notion AI requests and responses used for the feature.
Notion’s published timeline says Fireworks first told it on the evening of November 2 that a small amount of data had been accessed by malicious actors. Notion says it initially understood that data to be synthetic testing material. On November 3, it says it disconnected its systems from Fireworks, deleted data in Fireworks’ system and halted communication and training runs. Notion updated its advisory on November 10 and 11 to add information about the dataset and the affected transcripts.
Fireworks’ own incident update, as described in the source material, was last updated November 9 and said it had not detected an impact to Inference, Training SDK and Nexus, which it describes as zero-retention by default. Fireworks also said datasets were among the data accessed for certain customers. The two published descriptions do not establish which system retained Notion’s data, so the specific technical path remains unresolved.
““Unfortunately, during our investigation we learned that data was retained from the Fireworks endpoints that we used.””
— Notion
What the Breach Notice Leaves Open
Notion has not disclosed which Fireworks system retained the data, how long it was retained or the number of users whose transcripts were included. Its estimate covers fewer than 1% of Notion workspaces, but the notice does not give an exact workspace count or a total number of affected people. It also remains unclear what proportion of the transcripts contained sensitive information.
The published accounts do not explain how the data-retention incident relates to Fireworks’ statement that certain services are zero-retention by default. Neither company has identified the specific endpoint or system involved in retaining Notion’s data. The available information also does not establish whether other Fireworks customers experienced a similar issue. Those questions should not be treated as resolved by Notion’s workspace estimate or Fireworks’ description of its services.
Vendor Audit and Customer Reviews
Notion says it is auditing critical vendors and data processors for compliance with data-minimization practices, including zero-retention policies. Affected workspace users should follow the company’s Security incident review guidance, examine the relevant data and rotate credentials that may have appeared in chats. Notion says it has revoked exposed API keys found in affected messages.
Further clarity depends on additional disclosures from Notion or Fireworks about the system involved, the retention period and the scope of the affected dataset. Notion’s advisory may also be updated as its vendor audit and incident review continue. No further technical explanation or confirmed affected-user total is provided in the source material.
Key Questions
What Notion data was involved?
Notion says the dataset accessed by attackers included Notion AI chat transcripts used for the Insights feature. It defines a transcript as model input or output written to the chat, which may contain sensitive text.
How many Notion workspaces are affected?
Notion estimates that fewer than 1% of workspaces are affected. It has not published an exact count of workspaces or individual users in the source material.
Were Notion AI Meeting Notes affected?
Notion says AI Meeting Notes were not affected unless their audio, transcripts or summaries were used as input in a Notion AI chat transcript. It says no other Notion features were affected.
What should affected users do?
Notion advises affected users to review the data as if it were exposed and rotate passwords, API keys and other credentials pasted into Notion AI during the incident. It also says exposed API keys found in affected messages were revoked on November 11.
What remains unknown about Fireworks’ data retention?
The companies have not identified which Fireworks system retained the data, how long it was held, how many people were affected or whether other Fireworks customers faced the same problem.
Source: ThorstenMeyerAI.com